SAML
Contents
Where is this feature available?
Free / Open-source
Paid
Boost
Scale
Enterprise


Security Assertion Markup Language (SAML) enables users to access multiple systems with a single set of credentials. This is helpful for growing organizations that require centralized user management in an Identity Provider (IdP).
If you are configuring IdP-based SSO for the first time, we recommend you use OIDC, because it is generally considered more secure and simpler to operate than SAML.
Prerequisites
If you are using PostHog cloud, your organization must be subscribed to a platform package that offers SAML. If you are self-hosting PostHog, your instance must have an enterprise license that supports SAML.
You need to verify domains for any email address that you want to allow users to log in with. For example, if you want to allow users with an
@example.comemail address to log in, likejohn@example.com, you need to add and verifyexample.comas an authentication domain.If you are self-hosting PostHog, make sure you have properly set up your
SITE_URLenvironment variable configuration.If you are self-hosting PostHog, your PostHog instance must be accessible from the public internet over TLS.
Configuring SAML
Navigate to your organization's authentication settings page in PostHog.
Scroll down to the SAML section, and select Configure.
In your IdP, create a new SAML app for PostHog.
a. Copy the "ACS Consumer URL", "Audience / entity ID", and "Relay state" displayed in PostHog into your SAML app's configuration in your IdP.
b. Copy the following values from your SAML app's configuration in your IdP into PostHog:
ACS URL (also called Sign-on URL or SAML endpoint)
Entity ID (also called Issuer, IdP issuer, or Azure AD Identifier)
X.509 certificate used to verify SAML assertions
Your IdP might provide these values in an XML metadata file. If the certificate is provided as a file, open it in a text editor and copy its contents without changing the spaces or line breaks. The
BEGIN CERTIFICATEandEND CERTIFICATElines are optional.
c. Verify that your IdP shares the following attributes in the SAML assertion with PostHog:
Attribute Default name in PostHog Optional? Permanent ID name_id❌ No Email email❌ No First (given) name first_name❌ No Last name (surname) last_name✅ Yes Select Save.
Example: OneLogin
OneLogin quick setup
You can quickly connect OneLogin and PostHog by using the prebuilt integration.
In OneLogin admin, go to Applications and click Add App. Search for
PostHogand create your app.Go to the Configuration tab and where it says "PostHog domain name" enter your PostHog's instance domain (as it's also specified in the
SITE_URLenvironment variable), but don't include any protocol or trailing slashes. Examples:playground.posthog.com,myposthog.mydomain.com,myposthogdomain.com.Go to the SSO tab. This is where you'll obtain the information you need to pass to PostHog.
- Issuer URL needs to be set as SAML Entity ID.
- SAML 2.0 Endpoint (HTTP) needs to be set as SAML ACS URL.
- On X.509 Certificate click on View Details. Copy the full certificate and set it as SAML X.509 certificate.
You're good to go! Click Login with SSO in PostHog's login page.
OneLogin advanced
Use this option if you want to add additional configurations to your app that are not supported with the default app catalog.
In OneLogin admin, go to Applications and click Add App.
Search for
SAMLand select SAML Custom Connector (Advanced). Set name toPostHog.Go to the Configuration tab and edit the following attributes (leave everything else as default)
- In the Audience (EntityID) enter
https://us.posthog.com.- If you are using our EU deployment, use
https://eu.posthog.com. - If you are self-hosting, enter the exact same value as your
SITE_URLenvironment variable.
- If you are using our EU deployment, use
- Set the ACS (Consumer) URL Validator to a regex that only matches
<yourdomain>/complete/saml/. For instance:^https:\/\/us.posthog.com\/complete\/saml\/$(or useeufor an EU instance) - Set the ACS (Consumer) URL to
https://us.posthog.com/complete/saml/.- If you are using our EU deployment, use
https://eu.posthog.com/complete/saml/. - If you are self-hosting, use
<yourdomain>/complete/saml/.
- If you are using our EU deployment, use
- In the Audience (EntityID) enter
Go to the Parameters tab. You will add the following parameters. Be sure to check "Include in SAML assertion".
emailto match the user's email ("Email")first_nameto match the user's first name ("First Name")last_nameto match the user's last name ("Last Name")
Go to the SSO tab. This is where you'll obtain the information you need to pass to PostHog.
- Issuer URL needs to be set as SAML Entity ID.
- SAML 2.0 Endpoint (HTTP) needs to be set as SAML ACS URL.
- On X.509 Certificate click on View Details. Copy the full certificate, removing the first and last lines and set it as SAML X.509 certificate.
You're good to go! Click Login with SSO in the login page.
Example: Okta
In Okta admin, go to Applications and select Create App Integration.

Select the SAML 2.0 option for sign-in method.

Select Next, name the configuration PostHog, then select Next again.

Navigate to your PostHog organization's authentication settings, scroll down to SAML, then select Configure.


Copy the ACS consumer URL from PostHog into the Okta app's Single sign-on URL field, and copy the Audience / entity ID from PostHog into the Okta app's Audience URI (SP Entity ID) field.

In Okta, select Next. Check the box that says This is an internal app that we have created, then select Finish.

Copy the Sign on URL from Okta to the SAML ACS URL field in PostHog, the Issuer from Okta to the SAML entity ID field in PostHog, and the Signing Certificate from Okta to the SAML X.509 certificate field in PostHog.
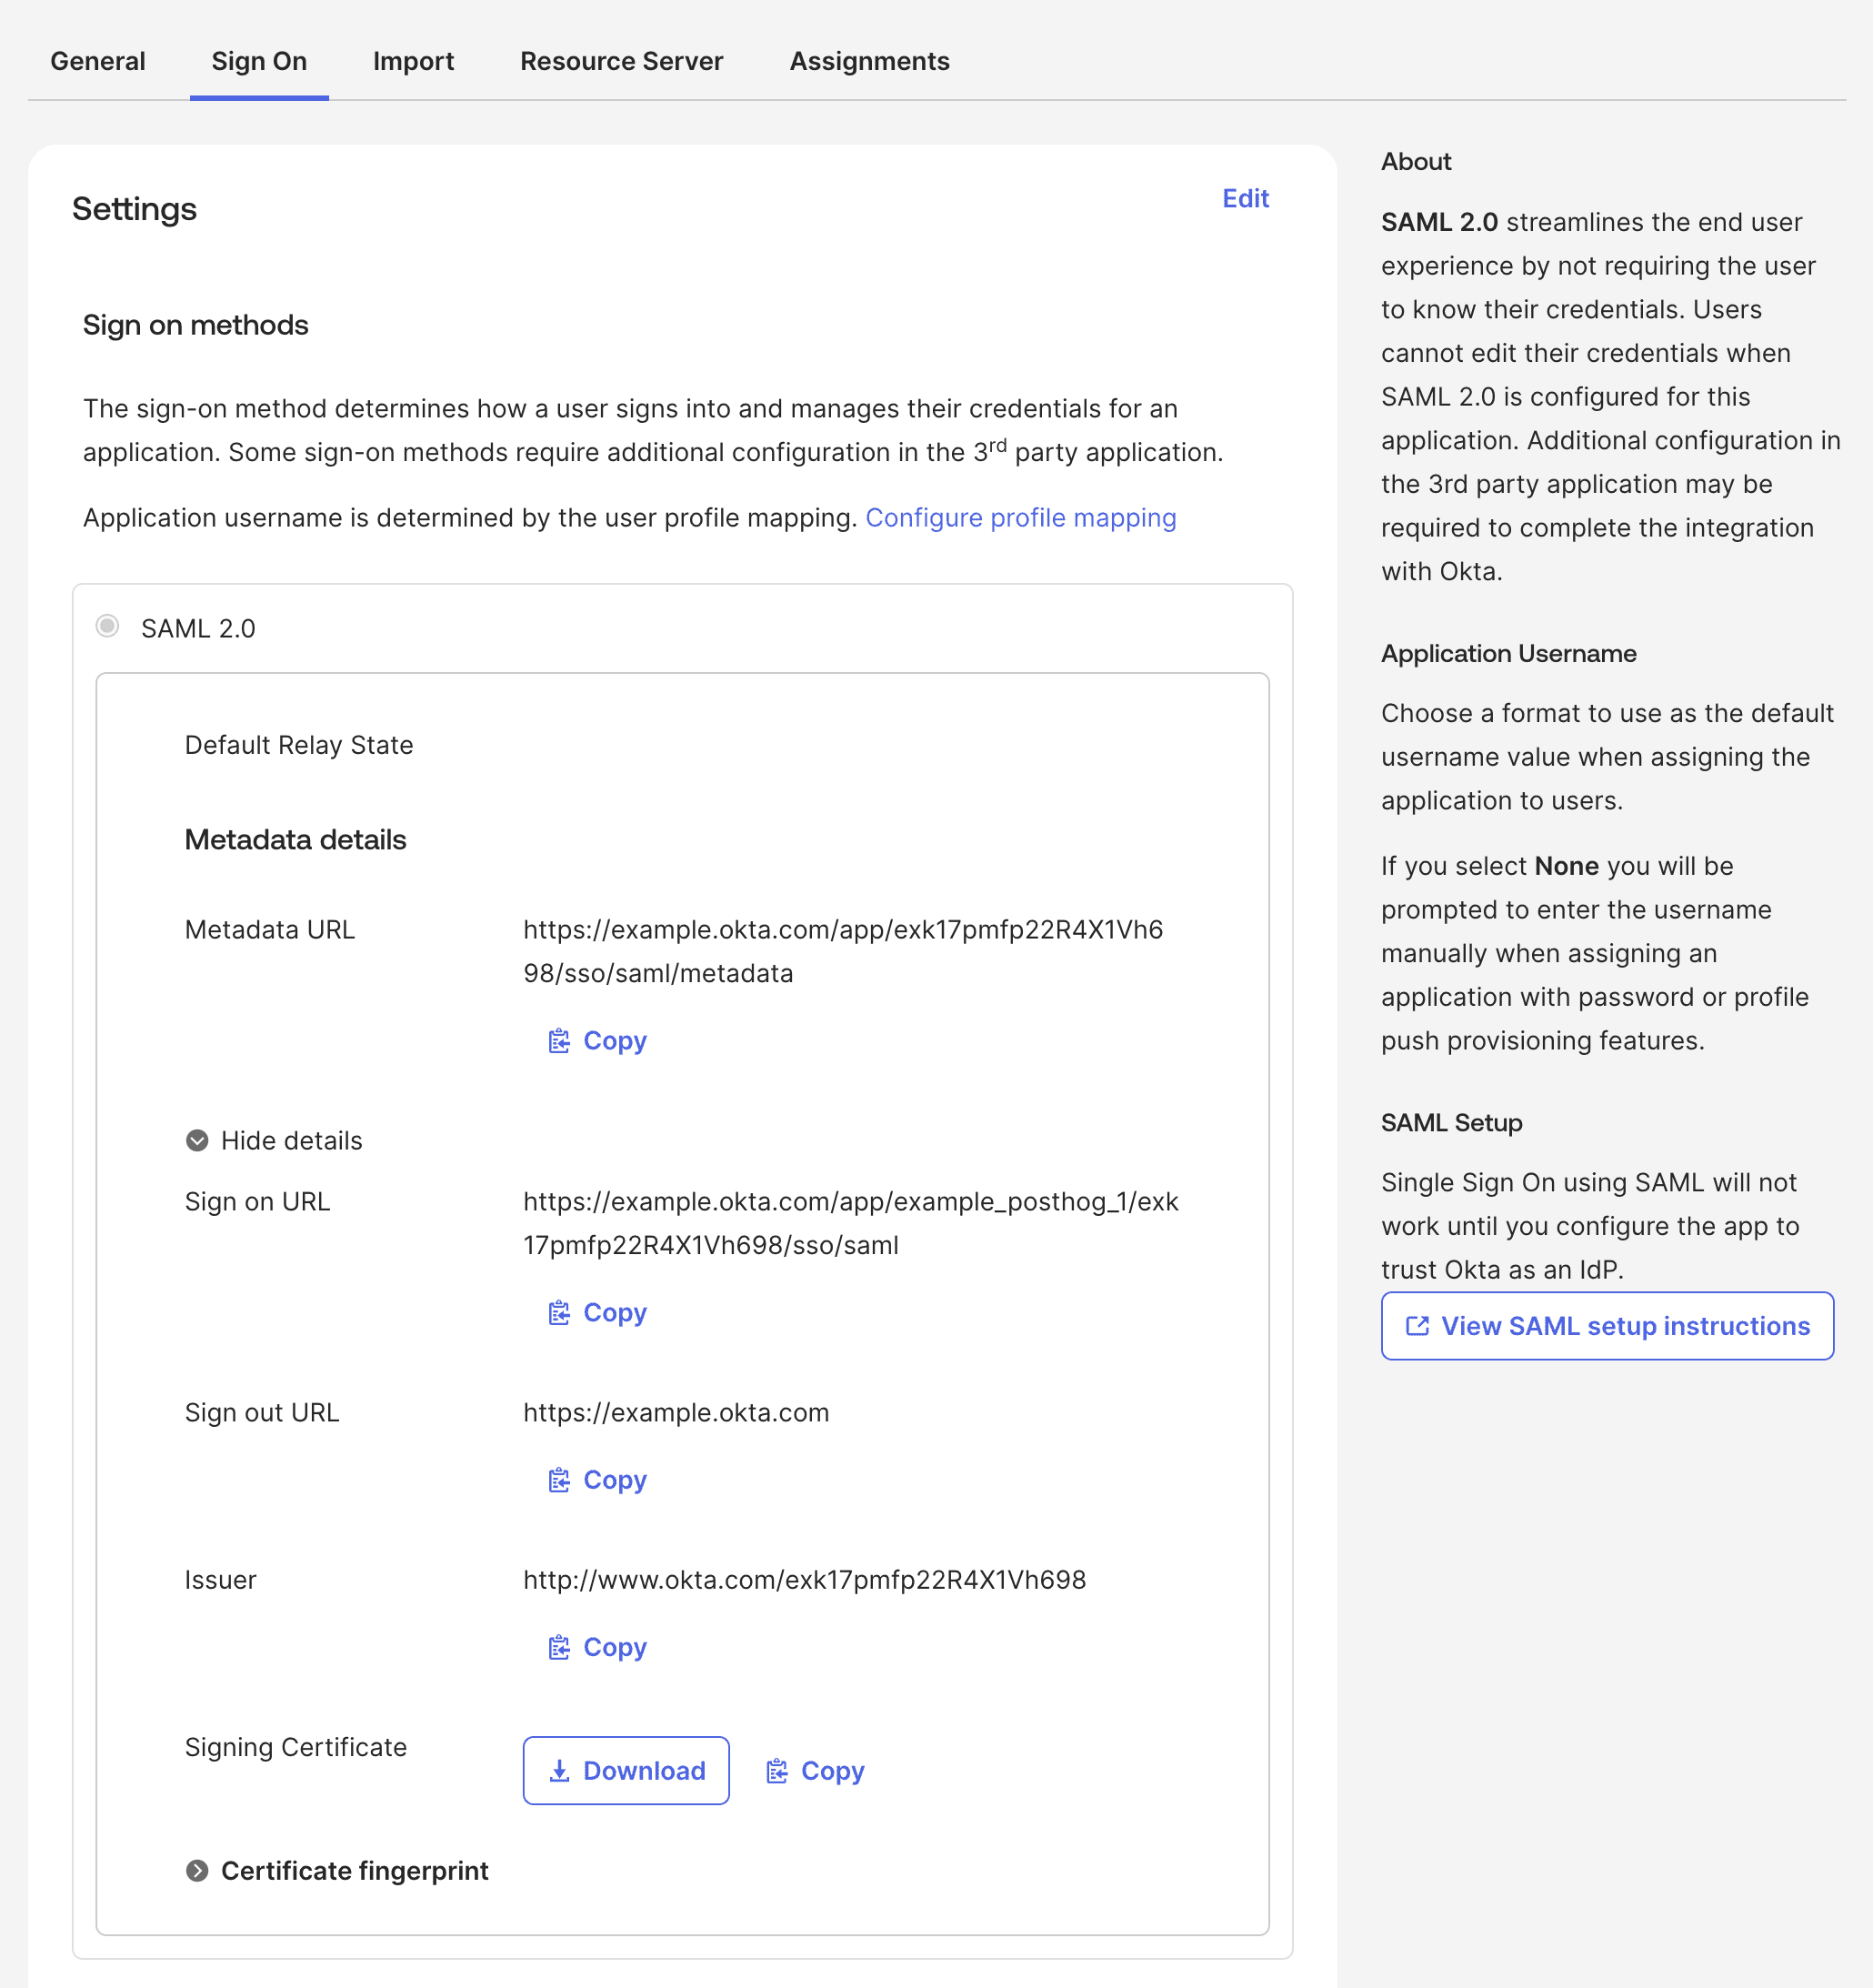
Select Save configuration in PostHog.


In Okta, navigate to the Sign On tab of your SAML app, then select Edit in the Settings section.
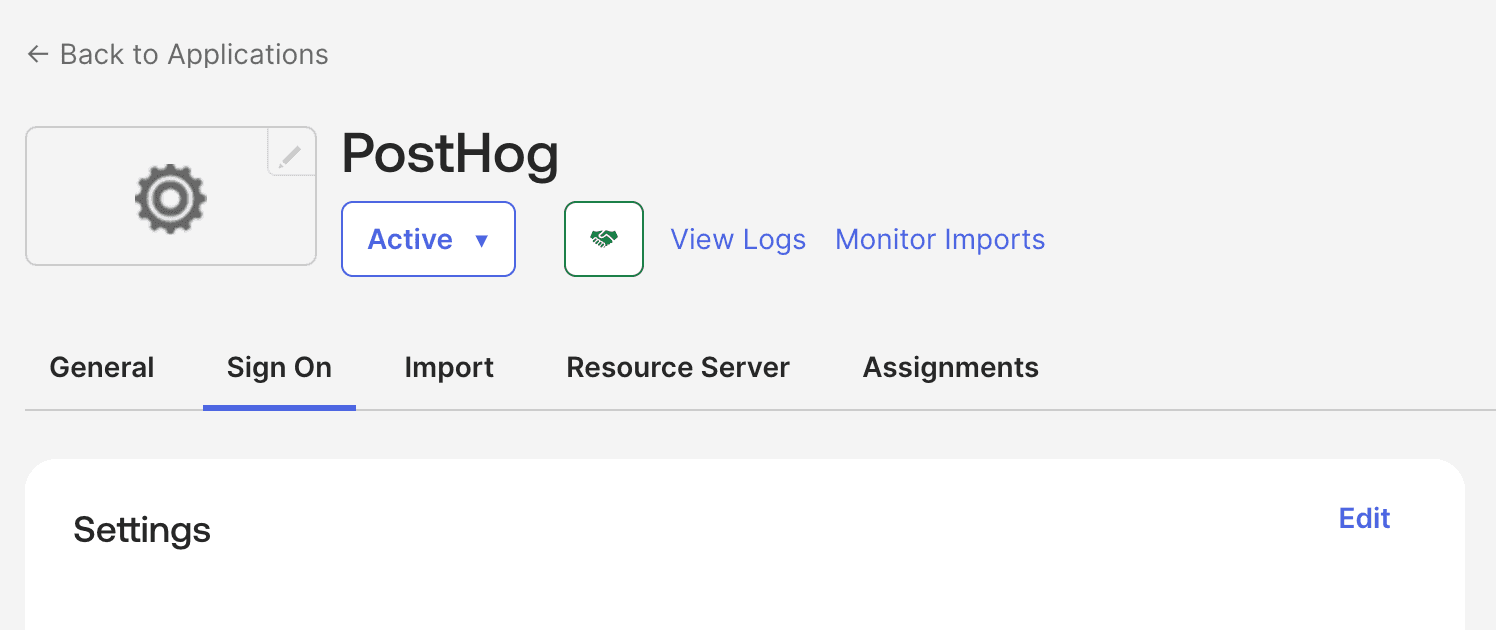
Copy the Relay state from PostHog to the Default Relay State field in Okta. Select Save

In Okta, scroll down to Attribute Statements add the following statements:
Name Expression email user.profile.email first_name user.profile.firstName last_name user.profile.lastName 
The next time you enter your email address during login, you will see an option to login using SAML.
Warnings
When using SAML to authenticate users in PostHog, there are a few considerations to keep in mind:
Only use SAML with identity providers you trust and that verify the user's email address. During login we use the email address provided by the identity provider. An untrusted identity provider could spoof a user's email address to impersonate your users.
Enabling or enforcing SAML will not disable Personal API Key usage. Users can authenticate with the PostHog API using their API keys without first authenticating via SAML. You can use ID-JAG (XAA) to programmatically restrict API access using policies defined in your identity provider.
Our SAML integration only handles authentication and user provisioning. It does not handle user removal. You can use SCIM to automatically deprovision users.
When you enable or enforce SAML, any existing user passwords are saved. If you disable SAML SSO in the future, your users will be able to login using their pre-existing password credentials.